Compliance Overview
Praxi helps your practice meet Australian healthcare compliance requirements, including AHPRA registration, Privacy Act obligations, and clinical record-keeping standards. Our compliance framework is designed specifically for Australian mental health practices, ensuring you meet all federal and state regulatory obligations.
Critical Retention Requirement — Australian healthcare providers must retain clinical records for a minimum of 7 years from the date of last contact for adult clients. For minors, records must be kept until the client reaches 25 years of age, or for 7 years from last contact, whichever is later. Failure to comply can result in regulatory action and professional misconduct findings. :::
Australian Regulatory Framework
Mental health practices in Australia operate under multiple overlapping regulatory frameworks. Praxi helps you navigate and comply with all of them.
Key Legislation
| Legislation | Jurisdiction | Key Requirements |
|---|---|---|
| Privacy Act 1988 | Federal | Australian Privacy Principles (APPs), mandatory data breach notification |
| Privacy Act 2025 (Amendment) | Federal | Right to erasure, enhanced consent requirements |
| Health Records Acts | State/Territory | Clinical record standards, access, retention |
| Health Insurance Act 1973 | Federal | Medicare claiming, provider eligibility |
| NDIS Act 2013 | Federal | Registered provider requirements, pricing rules |
| Mental Health Acts | State/Territory | Involuntary treatment, reporting obligations |
| Health Practitioner Regulation National Law | National | AHPRA registration, professional standards |
Regulatory Bodies
| Body | Role | Relevance |
|---|---|---|
| AHPRA | Practitioner registration | Registration verification, conditions monitoring |
| OAIC | Privacy oversight | Data breach notification, privacy complaints |
| Medicare Australia | Health claims | Provider numbers, claiming compliance |
| NDIS Quality & Safeguards Commission | NDIS oversight | Provider registration, incident reporting |
| State Health Complaints Commissioners | Complaints | Complaint investigation, practice standards |
Compliance Framework
| Requirement | Regulation | Praxi Feature |
|---|---|---|
| Practitioner registration | AHPRA | Registration tracking, expiry alerts |
| Privacy protection | Privacy Act 1988 | Data encryption, access controls |
| Clinical records | State health records acts | Note signing, audit trails |
| Data retention | 7+ years (adults), 25+ years (minors) | Automated retention policies |
| Medicare compliance | Health Insurance Act 1973 | MBS validation, claiming rules |
| NDIS compliance | NDIS Act 2013 | Service agreements, price guides |
Compliance Dashboard
Access the compliance dashboard at Settings → Compliance:
| Section | Purpose |
|---|---|
| Registration Status | AHPRA, insurance, NDIS, working with children |
| CPD Progress | Per-practitioner CPD hours against their annual target |
| Supervision Status | Supervision relationships and pending sign-offs |
| Unsigned Notes Summary | Notes past the 24-hour AHPRA signing deadline, grouped by practitioner |
| Compliance Alerts | Expiring credentials, overdue notes |
The audit trail lives at Monitoring → Audit Trail, and retention/erasure management at Settings → Privacy — see the pages linked below.
Key Compliance Areas
Practitioner Credentials
Track and manage:
- AHPRA registration numbers and expiry
- Professional indemnity insurance
- Working with Children checks
- Medicare provider numbers
- Specialist registrations
Organisation Insurance Register
In addition to practitioner-level insurance, Praxi includes an organisation-level insurance register for managing practice-wide policies (professional indemnity, public liability, cyber and data breach, building and contents, business interruption, and management liability). Track policy details, renewal dates, verification status, and receive tiered renewal reminders at 90, 60, 30, 14, and 7 days before expiry.
Learn more about AHPRA compliance →
Clinical Record Keeping
Australian standards require:
| Standard | Requirement | Praxi Implementation |
|---|---|---|
| Timeliness | Notes within 24 hours | Unsigned note reminders |
| Accuracy | Factual, objective content | AI-assisted review |
| Completeness | All relevant information | Required field validation |
| Security | Protected from unauthorised access | Role-based access, encryption |
| Retention | Minimum periods by patient type | Automated retention rules |
Privacy Act Compliance
The Privacy Act 1988 (Cth), as amended by the Privacy Act 2025, establishes 13 Australian Privacy Principles (APPs) that govern how health service providers collect, use, disclose, and store personal information. As a health service provider, your practice handles "sensitive information" (including health information), which attracts additional protections under APP 3. The 2025 amendment introduced a formal right to erasure for individuals, which Praxi supports through its erasure request workflow (see Data Retention for details).
Praxi implements all applicable Australian Privacy Principles:
| Principle | Requirement | Praxi Implementation |
|---|---|---|
| APP 1 | Open and transparent management | Privacy policy templates, privacy collection notices |
| APP 2 | Anonymity and pseudonymity | Not applicable to health records (exemption applies) |
| APP 3 | Collection of sensitive information | Consent tracking, collection purpose documentation |
| APP 4 | Dealing with unsolicited information | Incident logging, destruction workflows |
| APP 5 | Notification of collection | Client intake notices, consent forms |
| APP 6 | Use and disclosure | Third-party disclosure register, purpose limitation, audit logging |
| APP 7 | Direct marketing | Marketing consent separate from clinical consent |
| APP 8 | Cross-border disclosure | Data residency policy, cross-border transfer risk assessment, consent workflows |
| APP 9 | Government identifiers | Medicare numbers encrypted, access logged |
| APP 10 | Quality of personal information | Data validation, update prompts |
| APP 11 | Security of personal information | AES-256 encryption, role-based access, audit trails |
| APP 12 | Access to personal information | Client portal access, record export |
| APP 13 | Correction of personal information | Amendment workflows, correction tracking |
Mandatory Data Breach Notification
Under the Notifiable Data Breaches (NDB) scheme, you must notify the OAIC and affected individuals of eligible data breaches within 30 days. Praxi provides:
- Real-time security monitoring and alerting
- Breach assessment workflows
- Notification template generation
- OAIC reporting assistance
Audit Logging
Every action is logged:
- Who performed the action
- What was accessed or changed
- When it occurred
- From which device/location
Data Retention
Automated retention management:
| Record Type | Minimum Retention |
|---|---|
| Adult clients | 7 years from last contact |
| Minors | Until age 25, or 7 years (whichever later) |
| Medicare claims | 2 years from claim date |
| Financial records | 7 years |
Learn more about data retention →
Compliance Alerts
Alert Types
| Alert | Trigger | Priority |
|---|---|---|
| AHPRA expiring | 60, 30, 14, and 7 days before expiry | High |
| Insurance expiring | 90, 60, 30, 14, and 7 days before expiry | High |
| Unsigned notes | 24 hours after appointment | Medium |
| Missing consent | Client without signed consent | Medium |
| Incomplete records | Missing required fields | Low |
Alert Configuration
Compliance alert recipients and channels are configured from Settings → Compliance. Choose which staff members receive each alert type and select your preferred notification channels (in-app, email, or SMS for critical items).
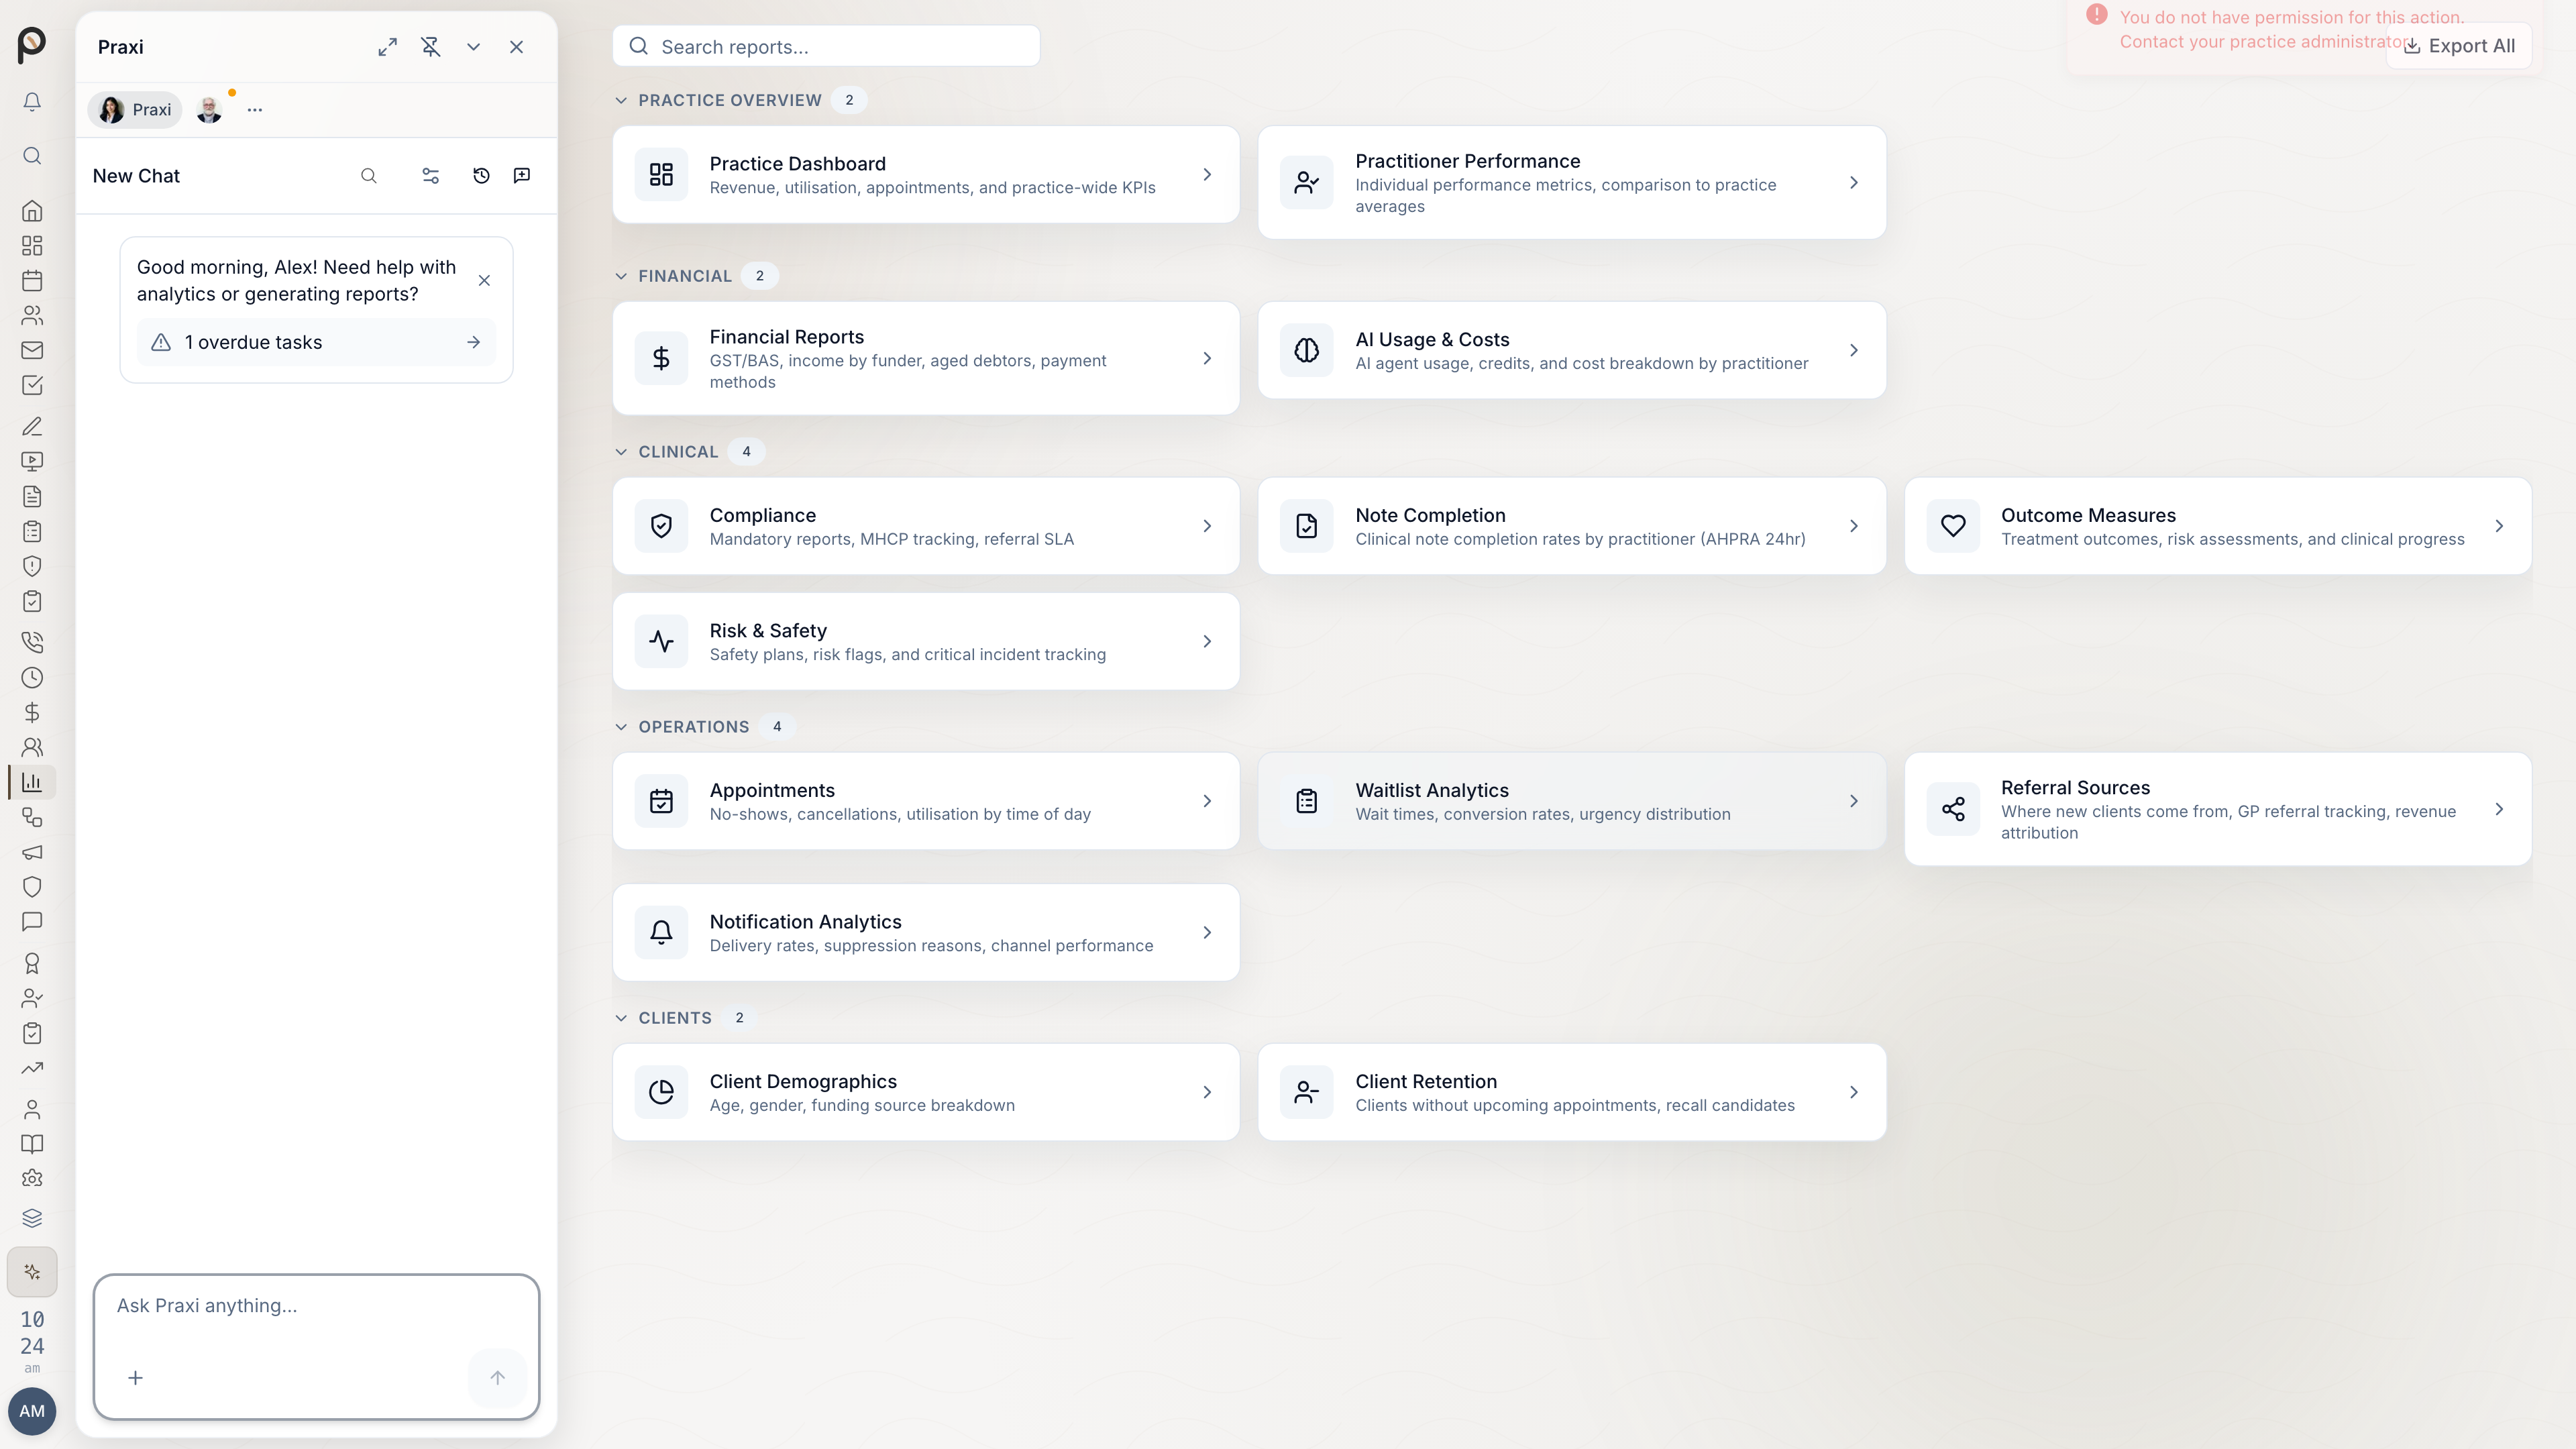
Compliance Reports
Available Reports
| Report | Purpose | Frequency |
|---|---|---|
| Credential Status | All practitioner registrations | Monthly |
| Unsigned Notes | Notes awaiting signature | Weekly |
| Consent Audit | Client consent status | Monthly |
| Access Log | Who accessed what | On demand |
| Data Retention | Records approaching limits | Quarterly |
Generating Reports
- Go to Reports → Compliance
- Select report type
- Set date range
- Choose format (PDF, CSV)
- Generate and download
Role-Based Access
Permission Levels
| Role | Compliance Access |
|---|---|
| Practice Owner | Full access to all compliance features |
| Supervisor | View team compliance, own credentials |
| Practitioner | Own compliance status only |
| Receptionist | No compliance access |
| Accountant | Financial compliance only |
Sensitive Information
Certain data has additional restrictions:
- Mental health records (additional consent required)
- Minor client records (guardian consent)
- Couples/family notes (shared consent)
Medicare Compliance
Claiming Rules
| Rule | Praxi Enforcement |
|---|---|
| Valid referral | Referral validation before claim |
| Session limits | Session count tracking |
| Item number rules | MBS compatibility checking |
| Provider eligibility | Medicare provider number validation |
Mental Health Treatment Plan
Track Better Access sessions:
- 10 individual sessions per calendar year
- 10 group sessions per calendar year
- Referral validity (6-12 months)
- Review requirements
NDIS Compliance
Provider Requirements
| Requirement | Implementation |
|---|---|
| NDIS registration | Provider number tracking |
| Service agreements | Template and tracking |
| Price guide adherence | Automatic price updates |
| Cancellation policy | NDIS-compliant rules enforced |
| Invoice requirements | Compliant invoice generation |
Record Keeping
NDIS requires:
- Service delivery records
- Progress notes
- Incident reports
- Complaints register
Praxi also runs automated compliance checks internally across security, data integrity, and privacy categories to ensure the platform meets Australian healthcare regulatory requirements on your behalf.
Safety and Risk Management
Praxi includes dedicated safety and risk management tools for clinical governance:
Clinicians record their own domain risk judgements and formulation. Praxi does not calculate an overall clinical risk rating or generate risk judgements with AI. Crisis alerts and questionnaire or form review signals remain available for a clinician to review and act on.
| Feature | Purpose |
|---|---|
| Safety Risk Dashboard | Centralised view of active crisis alerts, risk flags, and overdue safety plans |
| Safety Plans | Create and manage Stanley-Brown format safety plans with scheduled reviews and PDF/HTML export |
| Mandatory Reporting | Structured workflow for mandatory reporting with jurisdiction-aware guidance, encrypted PHI, and auto-generated compliance tasks |
| AHPRA Mandatory Notifications | Track and submit mandatory notifications to AHPRA for notifiable practitioner conduct under National Law s140-143 |
| Subpoena Management | Full subpoena lifecycle from intake through AI-assisted review, redaction, privilege review, and document bundling |
| Third-Party Disclosure Register | APP 6 compliant register of all disclosures to third parties with legal basis tracking and client notification status |
| Data Residency Controls | APP 8 cross-border disclosure compliance including transfer risk assessment, consent workflows, and geographic enforcement |
Learn more about mandatory reporting →
Learn more about subpoena management →
Continuous Compliance
Best Practices
- Regular reviews - Monthly compliance dashboard check
- Proactive renewals - Address alerts before expiry
- Staff training - Ensure team understands requirements
- Documentation - Keep policies current
- Audit preparation - Maintain audit-ready records
Compliance Calendar
| Month | Task |
|---|---|
| January | Annual compliance review |
| March | Insurance renewal (common) |
| June | AHPRA renewal (common) |
| July | Financial year compliance check |
| September | WWCC renewal (varies by state) |
| December | End-of-year audit preparation |
Professional Standards and Codes
AHPRA Professional Standards
All registered health practitioners must comply with their respective board's professional standards and codes of conduct. Key requirements include:
| Standard | Requirement | Praxi Support |
|---|---|---|
| Record keeping | Accurate, contemporaneous, legible | Structured templates, timestamps, digital signing |
| Confidentiality | Protect client information | Encryption, access controls, audit logging |
| Informed consent | Document consent for treatment | Consent tracking, digital signatures |
| Professional boundaries | Appropriate therapeutic relationships | Separate clinical and billing records |
| Supervision | Provisionally registered practitioners | Supervision logging, progress tracking |
Psychology Board Specific Requirements
For psychologists, additional requirements include:
- Client records must include assessment, formulation, intervention, and outcome data
- Progress notes within 24 hours of session (AHPRA guideline)
- Supervision documentation for registrars (minimum hours, competency tracking)
- Mandatory reporting of certain conditions
Getting Help
Support Resources
| Resource | Contact | When to Use |
|---|---|---|
| AHPRA | 1300 419 495 | Registration queries, conditions, notifications |
| Medicare Provider Line | 132 150 | Provider numbers, claiming rules |
| OAIC | 1300 363 992 | Privacy complaints, data breach guidance |
| NDIS Commission | 1800 035 544 | NDIS provider requirements, incidents |
| State Health Complaints | Varies by state | Client complaints, practice standards |
| Professional Association | APS, AASW, etc. | Professional guidance, ethics advice |
| Praxi Support | hey@praxi.au | System-specific compliance questions |
Compliance Contacts
Configure your practice compliance contacts from Settings → Compliance for quick reference and automated notifications. You can record your internal compliance officer, external legal advisor, insurance broker, accountant, professional association contact, and AHPRA notification contact, then set notification preferences for each.
Compliance Checklist
Use this checklist for regular compliance reviews:
Monthly
- Review AHPRA registration expiry alerts
- Check unsigned clinical notes
- Review missing consent forms
- Audit user access logs
Quarterly
- Full credential audit (all practitioners)
- Data retention policy review
- Insurance coverage verification
- Compliance report generation
Annually
- Privacy policy review and update
- Staff compliance training
- Full system audit
- Retention schedule review
- Disaster recovery testing